Testing Services
From penetration testing to Red Team simulation, from DDoS/DoS resilience tests to social engineering audits: we uncover your vulnerabilities and show you how to close them.
Explore services →We provide ISO 27001, KVKK and BİG Guide compliance consulting.
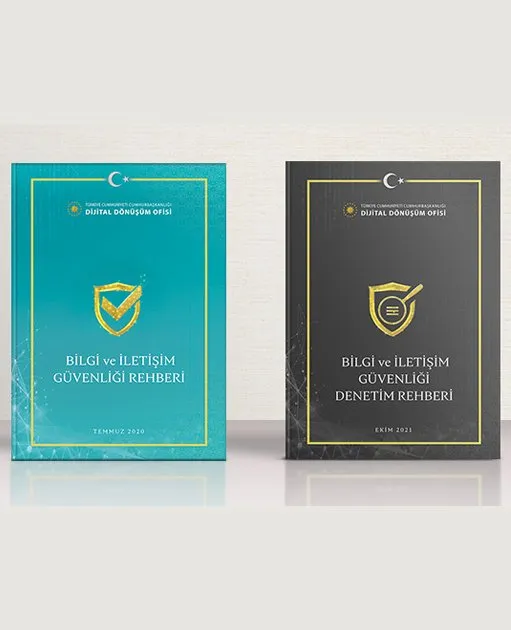
The Information and Communication Security (BİG) Guide sets out the information and communication security measures that public institutions and operators providing critical infrastructure services must comply with.
The BİG Guide was prepared under Presidential Circular No. 2019/12 of 06.07.2019, coordinated by the Presidency of the Digital Transformation Office (DDO) of the Republic of Türkiye, and approved on 24.07.2020.
Compliance with the measures in the Guide is mandatory for existing and new information systems at all public institutions and organizations and at operators providing critical infrastructure services.
Existing IT infrastructures are expected to be brought into line with these principles gradually, within the plan set out in the Guide and according to their security level priorities.
The benefits targeted by the Guide can only be achieved and sustained through effective audit and oversight.
To this end, the Presidency of the Digital Transformation Office prepared the Information and Communication Security Audit Guide to guide institutions and organizations in carrying out audits.
Public institutions and organizations and operators providing critical infrastructure services are expected to complete their compliance activities within the period specified in the Guide, and to carry out audits at least once a year to determine whether the activities performed and measures taken are adequate.
Our Information and Communication Security Guide compliance consulting follows these steps:
The ISO 27001:2022 Information Security Management System (ISMS) provides an international framework that ensures companies protect their financial data, intellectual property and sensitive customer information.
Organizations that establish an ISO 27001:2022 ISMS can identify and manage their information security risks, and so prevent unwanted incidents or minimize their impact.
Applied consistently, an ISO 27001:2022 system protects your company’s reputation and gives your customers and stakeholders confidence.
Our ISO 27001:2022 consulting methodology consists of the following phases:
In the preparation phase, the scope of the ISO 27001:2022 ISMS project is defined, the project team is oriented through information security training, and the organization’s management support is made concrete.
In the planning phase, a gap analysis is carried out to collect information on the organization’s business and legal requirements for information security, its IT infrastructure and its information security control points. Once the organization’s valuable assets are identified, an ISO 27001:2022 risk analysis establishes the current state and determines the needs for developing and improving controls.
In this step, the ISMS components covering management processes (policies, procedures, guidelines, etc.) and the controls found lacking in the risk analysis are developed and put into practice. Staff receive information security awareness training tailored to the organization’s needs.
An internal audit is carried out covering the whole of the ISO 27001:2022 standard and part of ISO 27002:2022, “Information Security Controls”. Management review steps identify the need for corrective and preventive actions.
In this final step of our ISO 27001 consulting, the necessary improvement plans are implemented in line with the corrective and preventive action requirements identified and reported by the various parties.
Protecting the privacy of personal data, such as a person’s identity, contact, health and financial information, private life, religious beliefs and political views, is a legal obligation for organizations.
Personal data is frequently processed by automated means through IT systems, in both the private and the public sector.
While using this information brings convenience and advantages for individuals and for providers of goods and services, it also brings the risk of the information being misused.
With our experienced team, we provide legal and technical consulting on KVKK (Turkey’s Personal Data Protection Law) process management and auditing.
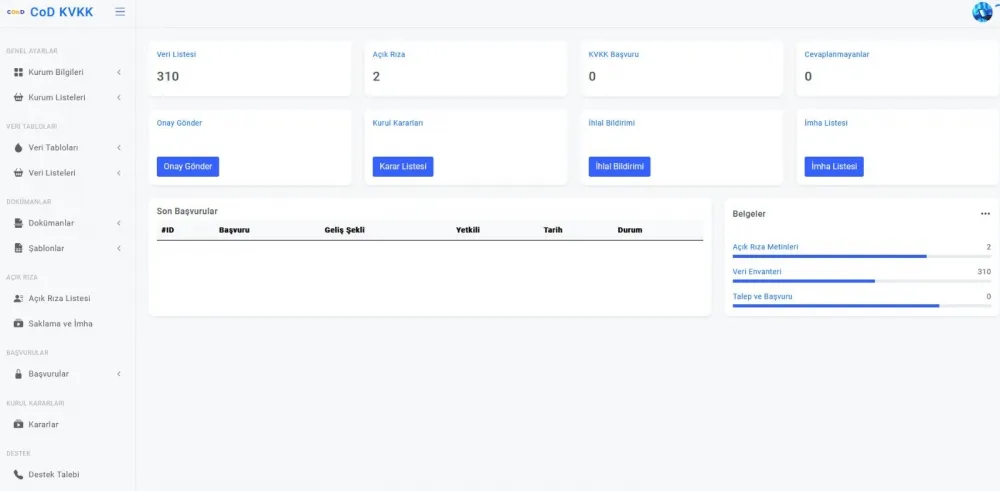
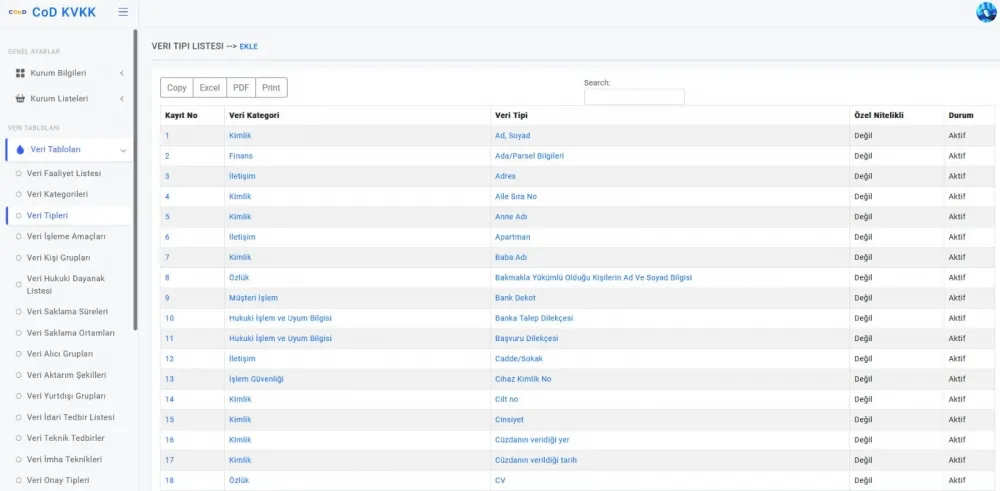
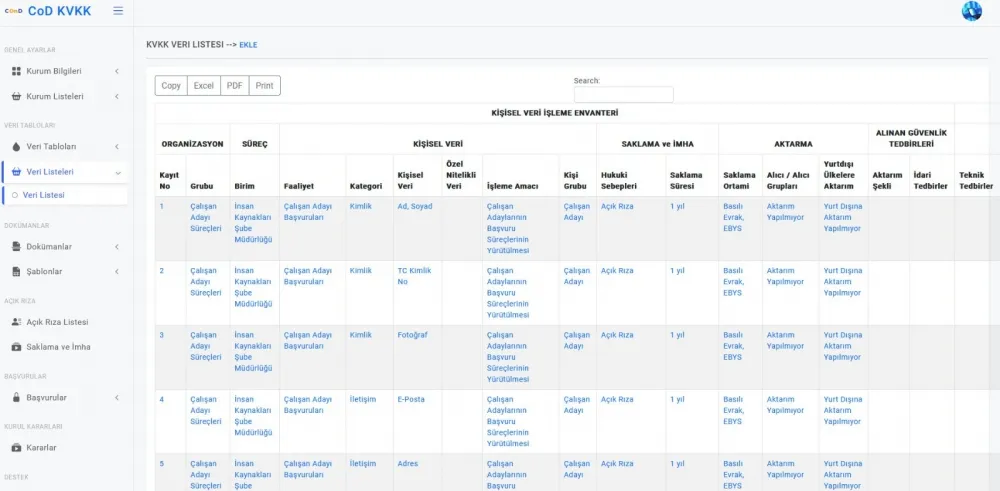
With the CenterOnDigital KVKK Compliance Process Management Software, developed as part of our in-house R&D, you can manage your organization’s KVKK processes easily, quickly and effectively.
Based on the organization’s personal data processing activities, the application builds a legally compliant Personal Data Inventory and automates data management processes, saving time, cost and workload.
From penetration testing to Red Team simulation, from DDoS/DoS resilience tests to social engineering audits: we uncover your vulnerabilities and show you how to close them.
Explore services →Information security maturity and cyber risk assessment, information asset inventory and classification, and IT health checks that reveal where you stand and what needs improving.
Explore services →